What Does HTTPS Mean? HTTP vs HTTPS Explained
HTTPS stands for Hypertext Transfer Protocol Secure. Learn how it works, how to spot it in your browser, and how it differs from HTTP.
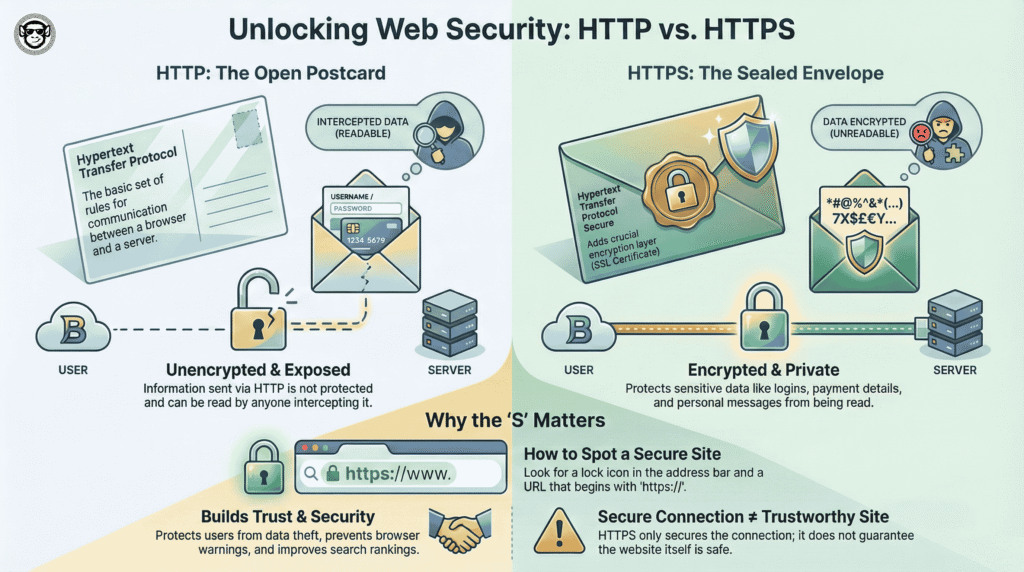
HTTPS stands for Hypertext Transfer Protocol Secure. It is HTTP, the protocol your browser uses to talk to websites, with encryption added. That encryption stops other people on the network from reading or changing what passes between your browser and the site.
The "S" means the connection is secure. It does not mean the website itself is trustworthy, and that difference matters. This guide explains what HTTPS is, how it works, how to spot it in your browser, and why almost every site uses it now.
Interested In Audio Format ?
HTTP vs HTTPS at a glance
| HTTP | HTTPS | |
|---|---|---|
| Full name | Hypertext Transfer Protocol | Hypertext Transfer Protocol Secure |
| Web address starts with | http:// | https:// |
| Data encrypted in transit | No | Yes, using TLS |
| Can others read or change the data on the way? | Yes | No, not without being detected |
| Needs a certificate | No | Yes |
| Default port | 80 | 443 |
| What browsers show | Often a "Not secure" warning | Treated as the normal, secure case |
| Today | Legacy; avoid for anything real | The standard for all websites |
A simple way to picture it
Think of HTTP as a postcard. Anyone who handles it on the way, from the sorting office to the postman, can read what is written on it, and could even change it.
HTTPS is a sealed envelope. The message is the same, but only the person it is addressed to can open it, and any tampering shows. The website's certificate is like a check that the address on the envelope really belongs to who it says it does.
How HTTPS works, step by step
When you open an https:// address, this happens in a fraction of a second:
- Your browser connects to the site's server, normally on port 443.
- The server presents its certificate. This is a digital document that ties the site's public key to its domain name.
- Your browser checks the certificate. It looks for a trusted issuer, a match with the domain you asked for, and that the certificate has not expired.
- The two sides agree on encryption keys. This exchange is called the TLS handshake.
- Data flows through the encrypted connection. Passwords, form entries and page content are scrambled in transit, so someone watching the network sees only unreadable data and cannot change it without being detected.
If the check in step 3 fails, for example because the certificate is expired or belongs to a different domain, the browser shows a full-page warning instead of loading the site.
One common slip is mixed content: an HTTPS page that loads an image or script over plain HTTP. Browsers either upgrade those requests to HTTPS or block them.
SSL, TLS and certificates: what is the difference?
You will see "SSL" and "TLS" used almost interchangeably, so here is the short version:
- SSL (Secure Sockets Layer) was the original encryption protocol for the web. It is obsolete.
- TLS (Transport Layer Security) is its successor, and it is what actually secures your connection today. TLS 1.3 is the current version, and TLS 1.2 is still widely used. Versions 1.1 and 1.0 should no longer be used.
- An "SSL certificate" is the everyday name for the certificate a site uses to prove its identity, even though the connection now runs on TLS. The name stuck.
TLS gives you three things:
- Encryption, so nobody can read the data in transit.
- Integrity, so the data cannot be altered without detection.
- Authentication, so you know you are talking to the real domain and not an imposter.
The third one relies on a certificate authority (CA): a trusted organisation that issues certificates after checking the applicant controls the domain. Your browser ships with a list of CAs it trusts, and it only accepts certificates issued by one of them. For more on how a domain name finds its server in the first place, see what DNS is.
How to tell if a site uses HTTPS
- Look at the address. It should start with
https://. Many browsers hide the prefix and show only the domain, so click the address bar to see the full URL. - Look at the icon next to the address. Browsers have traditionally shown a padlock for a secure connection. Since Chrome 117 (September 2023), Chrome shows a settings-style "tune" icon instead, because people kept reading the padlock as "this site is trustworthy". Clicking it still shows whether the connection is secure.
- Watch for warnings. A "Not secure" label or a full-page certificate error means the connection is not protected, or the certificate failed the browser's checks. Do not enter passwords or card details on that page.
- Inspect the certificate. Click the icon beside the address, open the connection details and look for the certificate. It shows who it was issued to, which authority issued it and when it expires. The exact menu names differ between browsers.
You can also run a site through a checker. Our free SSL checker guide walks through it.
Does HTTPS mean a website is safe?
No. This is the most common misunderstanding about HTTPS.
HTTPS tells you two things: the connection between you and the site is encrypted, and the certificate matches the domain you reached. It tells you nothing about what the site's owner intends to do with your data.
A phishing site can have a valid certificate, because certificates are available to anyone who controls a domain, and many are free. A scam shop can use HTTPS. A site hosting malware can too.
So treat HTTPS as a minimum requirement, not a seal of approval. Before trusting a site with sensitive information, also check:
- that the domain is spelled exactly as you expect, with no swapped or extra characters
- that you reached it from a link or bookmark you trust
- that the site's content, contact details and reputation look legitimate
Why every website should use HTTPS
It used to be that only shops and banks needed HTTPS. Now it is the default for everything, including simple blogs, for these reasons:
- It protects logins and payments. Anything a visitor types into a form is encrypted in transit.
- It protects visitors from tampering. On plain HTTP, a network operator or a hijacked Wi-Fi hotspot can read or alter pages on the way, for example by injecting ads or malicious scripts.
- It builds trust. Visitors who see a browser warning on your site often leave.
- Browsers expect it. Plain HTTP pages get flagged as not secure, and some modern browser features only work on HTTPS pages (so-called secure contexts).
- It helps with search. Google announced in August 2014 that HTTPS is a ranking signal. It is one signal among many and counts for far less than the quality and relevance of your content, so do not expect a ranking jump from it alone. It does remove a reason to be held back.
- It costs little or nothing. Free certificates are widely available, and most hosts include one.
How to get HTTPS on your own site
- Check your host first. Many hosting providers issue and renew a certificate for you with one click or automatically. If yours does, you are mostly done. If you are still choosing a host, our guide to domains vs hosting explains what each part does.
- Otherwise, use Let's Encrypt. It is a free, automated certificate authority run by the nonprofit ISRG. It uses a protocol called ACME and confirms you control the domain with a challenge, either a DNS record or a file served over HTTP. Most server tools can automate this and renew certificates for you.
- Redirect HTTP to HTTPS. Send visitors who arrive on
http://to thehttps://version with a permanent (301) redirect, so old links and bookmarks keep working. - Consider HSTS. The
Strict-Transport-Securityresponse header tells browsers to use HTTPS for your site from then on. Turn it on only once HTTPS works everywhere on the site, since it is hard to undo. - Fix mixed content. Make sure images, scripts and stylesheets all load over
https://, or the page will show warnings or have parts blocked. - Update your links. Change internal links, your sitemap and your Search Console property to the HTTPS version.
For how the server side fits together, see how web servers work.
Quick cheat sheet
| Term | What it means |
|---|---|
| HTTP | The protocol browsers use to talk to websites. Unencrypted. |
| HTTPS | HTTP plus encryption, using TLS. |
| SSL | The old encryption protocol. Obsolete; the name lives on in "SSL certificate". |
| TLS | The modern protocol that secures HTTPS connections. |
| Certificate | A digital document linking a site's public key to its domain name. |
| Certificate authority (CA) | A trusted organisation that issues certificates. |
| Padlock / site icon | Shows the connection is encrypted. Does not prove the site is trustworthy. |
| HSTS | A header telling browsers to always use HTTPS for a site. |
FAQ
What does the S in HTTPS stand for?
Secure. HTTPS is Hypertext Transfer Protocol Secure: HTTP with TLS encryption.
Is HTTPS the same as SSL?
No. HTTPS is the secure version of the web protocol. SSL is an older encryption technology that has been replaced by TLS. People still say "SSL certificate", but modern HTTPS connections use TLS.
Does HTTPS mean a website is safe?
No. It means your connection to the site is encrypted and the certificate matches the domain. A malicious site can also use HTTPS, so still check the domain and be careful what you share.
Does a small blog or personal site need HTTPS?
Yes. Even without logins or payments, HTTPS stops others altering your pages in transit, avoids browser warnings, and is expected by visitors and search engines. It is usually free.
How do I check a site's certificate?
Click the icon beside the address bar, open the connection or certificate details, and you can see who the certificate was issued to, who issued it and when it expires. Or use a free SSL checker.
Is HTTP ever okay?
For anything real, no. The only sensible uses are local testing and internal tools on a network you fully control, and even then HTTPS is better.



Join the conversation
What do you think?
Write a comment
No comments yet. Be the first to share a thought.